John Mills just put up the podcast for the first idCast discussion from yesterday. I really enjoyed talking with Jon, Gabe, Drummond, Scott, Mike, and Dmitry about OpenID. I think the discussion around XFN, microformats, and OpenID is just getting started. (And I apologize to everyone for my flaky mike or network or whatever the problem was -- Jon did a great job of cleaning things up.)
2007/02/22


The value of open identity
This seems to be turning into OpenID Month, but Fred Stutzman just posted a great explanatory article about OpenID at dev.aol.com: OpenID and the Value of Connected Identity. It does an especially nice job going beyond the single-signon aspect and talking about the value of connecting all your the various relationship networks together, with you in control over how they're used.
2007/02/21
Your blog is your OpenID
As of this morning's Journals update, you now have a couple of new choices to use for your OpenID:
When would you want to use one of these instead of http://openid.aol.com/screenname? It depends on what you're doing. If you're leaving a comment over on a LiveJournal, you may want to point back at your blog so they can come and comment on yours. This lets you do that in a verified way. If you have more than one blog, the first URL gives a synopsis of all your blogs, and you may want to hand that out instead. These are for experimentation only at this point and may change, so please don't use one of these for a permanent identity quite yet. They both delegate to http://openid.aol.com/screenname so all three are effectively transparent aliases of each other. Which one you use is up to you.
Another subtle change: When someone comments on your blog, their screen name now links to a search for their AOL Journals. So when you click on their signature, you can get to their list of blogs if they have any. This makes it slightly easier to go back and comment on their blog.
We're also experimenting with hCard support. The signatures on entries are marked up so that hCard processors will pick up on the fact that they name a person that has a URL -- and that URL is an OpenID. We don't do this for comments yet. I think we'd want to give commenters control over how much information gets published about them. Combining this with OpenID opens some very interesting possibilities. People who opt in would be able to verifiably link their comments across OpenID-enabled sites, automatically track responses to their comments, or find other people who write similar comments. And a lot more things I haven't thought of.
http://journals.aol.com/screenname
- or -
http://journals.aol.com/screenname/blogname
- or -
http://journals.aol.com/screenname/blogname
When would you want to use one of these instead of http://openid.aol.com/screenname? It depends on what you're doing. If you're leaving a comment over on a LiveJournal, you may want to point back at your blog so they can come and comment on yours. This lets you do that in a verified way. If you have more than one blog, the first URL gives a synopsis of all your blogs, and you may want to hand that out instead. These are for experimentation only at this point and may change, so please don't use one of these for a permanent identity quite yet. They both delegate to http://openid.aol.com/screenname so all three are effectively transparent aliases of each other. Which one you use is up to you.
Another subtle change: When someone comments on your blog, their screen name now links to a search for their AOL Journals. So when you click on their signature, you can get to their list of blogs if they have any. This makes it slightly easier to go back and comment on their blog.
We're also experimenting with hCard support. The signatures on entries are marked up so that hCard processors will pick up on the fact that they name a person that has a URL -- and that URL is an OpenID. We don't do this for comments yet. I think we'd want to give commenters control over how much information gets published about them. Combining this with OpenID opens some very interesting possibilities. People who opt in would be able to verifiably link their comments across OpenID-enabled sites, automatically track responses to their comments, or find other people who write similar comments. And a lot more things I haven't thought of.
2007/02/20
Digg += OpenID!
I'm about to run out the door, but just had to blog (flog?) this: Digg will support OpenID! This is obviously huge, and particularly cool for us considering the features we're about to put into production for AOL Journals tonight.
(There are so many OpenID announcements that I feel the need for shorthand. Thus, "X += OpenID", plus ! for a particularly good move.)
(There are so many OpenID announcements that I feel the need for shorthand. Thus, "X += OpenID", plus ! for a particularly good move.)
2007/02/16
AOL and 63 Million OpenIDs (from dev.aol.com)
I'm following up on the OpenID discussion over at dev.aol.com/blog:
Tags: OpenID, identity, social software, user centric identity
Yesterday, I blogged about AOL's work-in-progress on OpenID. It generated a lot of positive commentary.I realized after reading the reactions that I buried the lead: Thereare now 63 million AOL/AIM OpenIDs. Anyone can get one by signing upfor a free AIM account. This is cool.(full article)
Tags: OpenID, identity, social software, user centric identity
2007/02/14
AOL and OpenID: Where we are
 It's not really a secret that AOL has been experimenting with OpenID. As I've said, I think that user-centric, interoperable identity is hugely important to enable the social experiences we're trying to provide. This is a work in progress, but things are coming along thanks to our authentication team's diligent effort. Here's where we are today:
- Every AOL/AIM user now has at least one OpenID URI, http://openid.aol.com/<sn>.
- This experimental OpenID 1.1 Provider service is available now and we are conducting compatibility tests.
- We're working with OpenID relying parties to resolve compatibility issues.
- Our blogging platform has enabled basic OpenID 1.1 in beta, so every beta blog URI is also a basic OpenID identifier. (No Yadis yet.)
- We don't yet accept OpenID identities within our products as a relying party, but we're actively working on it. That roll-out is likely to be gradual.
- We are tracking the OpenID 2.0 standardization effort and plan to support it after it becomes final.
2007/02/11
How many different identities can one person sanely manage?
...asks John Udell, in Critical mass and social network fatigue. I'd argue that the answer is about one and a half, in the long run. (The Shockwave Rider pushed it a lot further, but then he was founding cyberpunk. Also, he was fictional.)
When "identity" was just basically a system-local nickname used between you and a service, having multiple names for yourself was a minor inconvenience at worst, and sometimes mildly useful for privacy. Now that the services are more and more intermediaries between people, nicknames are a problem. Jon notes:
While OpenID isn't a total solution for these issues, it's a critical piece of infrastructure. As an example of the kinds of things it enables, take a look at Jyte.
When "identity" was just basically a system-local nickname used between you and a service, having multiple names for yourself was a minor inconvenience at worst, and sometimes mildly useful for privacy. Now that the services are more and more intermediaries between people, nicknames are a problem. Jon notes:
Years ago at BYTE Magazine my friend Ben Smith, who was a Unixgreybeard even then (now he’s a Unix whitebeard), made a memorablecomment that’s always stuck with me. We were in the midst of evaluatinga batch of LAN email products. “One of these days,” Ben said in, Ithink, 1991, “everyone’s going to look up from their little islands ofLAN email and see this giant mothership hovering overhead called theInternet.”Yep. Email is still the killer app of the Internet, and it wouldn't be if it were still stuck in LAN mail silos. Though spam is now so bad that I literally can't send email to a few people who can't manage their spam filters. That's a real issue and represents a real opportunity as well.
While OpenID isn't a total solution for these issues, it's a critical piece of infrastructure. As an example of the kinds of things it enables, take a look at Jyte.
Subscribe to:
Posts (Atom)
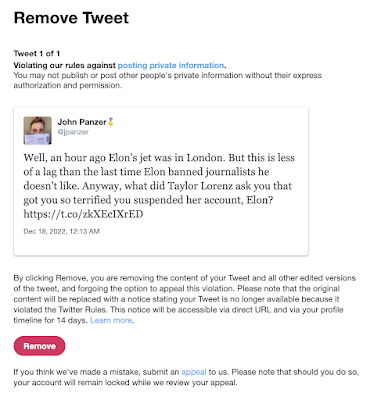
Suspended by the Baby Boss at Twitter
Well! I'm now suspended from Twitter for stating that Elon's jet was in London recently. (It was flying in the air to Qatar at the...
-
 Update 6/2/2023: I was right . These are my observations for our local conditions (Santa Clara County, July 10-12, 2020), which to summarize...
-
 Last night Rachel Maddow talked about an apparently fake NSA document "leaked" to her organization. There's a lot of info t...
-
Well! I'm now suspended from Twitter for stating that Elon's jet was in London recently. (It was flying in the air to Qatar at the...
