 It's nice to see something your team has worked on being put to good use. In addition to other things, we open sourced the JavaScript Compiler tool my group has used internally for several years. (It's actually more of a linker and compressor than a compiler since of course the output is still JavaScript.) We're also contributing new code to Dojo, including a pretty cool cross domain XML request mechanism.
2006/08/31
AOL's Open Source Contributions to Dojo
It's nice to see something your team has worked on being put to good use. In addition to other things, we open sourced the JavaScript Compiler tool my group has used internally for several years. (It's actually more of a linker and compressor than a compiler since of course the output is still JavaScript.) We're also contributing new code to Dojo, including a pretty cool cross domain XML request mechanism.

2006/08/28
Sam Ruby presents "Teenage Mutant CyberSurfers"
This afternoon, Sam Ruby was nice enough to reprise a version of his recent talk at AOL Silicon Valley. There's a real independent convergence between Sam's observations and predictions and the fictional world described in Vernor Vinge's Rainbows End. Which as I understand Sam is just now reading :).
Update: The audio is up on our podcast feed already!
Update: The audio is up on our podcast feed already!
2006/08/10
AOL Pictures Beta and woohoo
In conjunction with the new Pictures Beta, there's a cool tool called woohoo which displays a an AIMPages picture gallery in a widget, embeddable anywhere. Fun stuff... for example:
2006/08/02
Feeds Best Practices
The slides from my RSS/Atom Feeds Best Practices talk from lunch today are up now. There was a good discussion afterwards and hopefully we'll put up a podcast. I'm more convinced than ever that the key to a successful presentation is: free food.
2006/07/28
URL format change for Journals
One of the recent changes this week in Journals is an update to the format of our entry URLs. We're essentially adding the entry date and title to the URL, for example:
.../entries/2006/07/13/rest-and-the-authorization-header/1354
So anyone who may be parsing our URLs -- be aware that the format has changed :). We will, however, do a permanent redirect from the old URLs to the new ones.
.../entries/2006/07/13/rest-and-the-authorization-header/1354
So anyone who may be parsing our URLs -- be aware that the format has changed :). We will, however, do a permanent redirect from the old URLs to the new ones.
2006/07/13
REST and the Authorization: Header
Talking to lots of people about identity, mashups, web services, and sustainability of the mashup ecology today at Mashup Camp. I'm wondering why LID apparently is using a new X- header for passing pointers to authentication information rather than re-using the existing extensible Authorization: header. Both GData and Amazon Web Services allow Authorization: as at least one option in their REST interfaces:
Authorization: GoogleLogin auth ...
Authorization: AWS ...
I know that GData uses 401 Unauthorized and WWW-Authenticate: challenge headers and I'm going to assume that AWS does too:
WWW-Authenticate: AuthSub realm="https://www.google.com/accounts/AuthSubRequest"
So, existing services are using the RFC 2617 framework; it's working for them; why not build on top of that instead of inventing new headers?
2006/07/12
Mashup Camp: Identity and Access Control in Mashups
Some notes I just took for the AccessControl session (my first session of the camp). Here's a shot of the campers organizing the schedule an hour ago:

Subscribe to:
Posts (Atom)
Suspended by the Baby Boss at Twitter
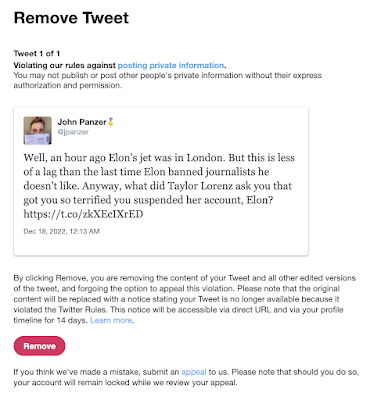
Well! I'm now suspended from Twitter for stating that Elon's jet was in London recently. (It was flying in the air to Qatar at the...
-
 Update 6/2/2023: I was right . These are my observations for our local conditions (Santa Clara County, July 10-12, 2020), which to summarize...
-
 Last night Rachel Maddow talked about an apparently fake NSA document "leaked" to her organization. There's a lot of info t...
-
Well! I'm now suspended from Twitter for stating that Elon's jet was in London recently. (It was flying in the air to Qatar at the...
